
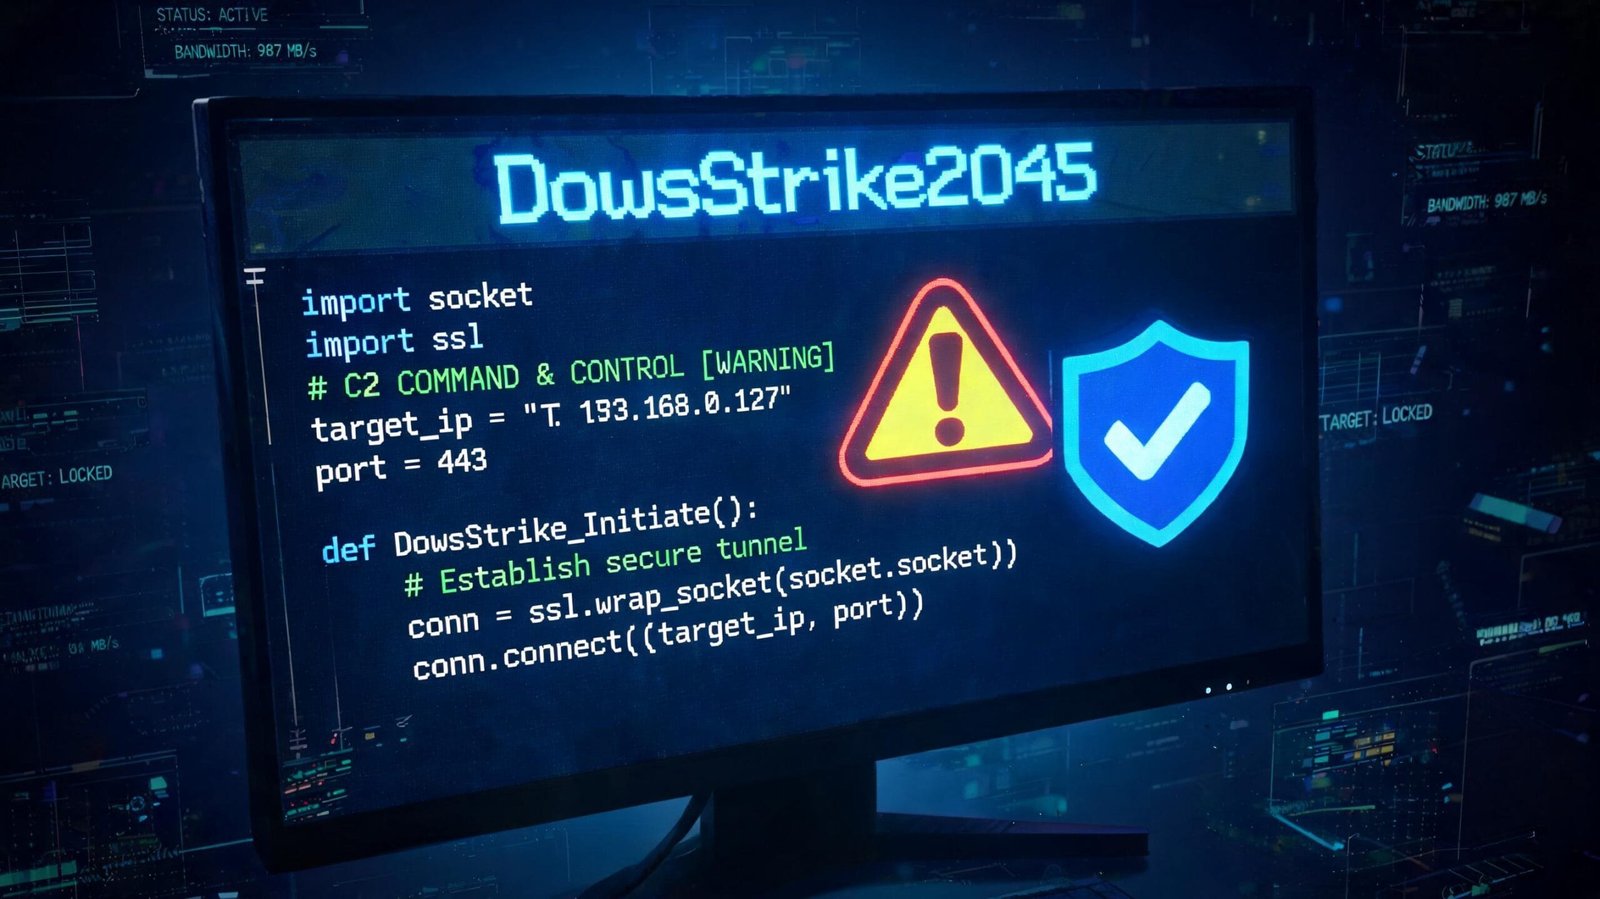
Searches for unusual technical phrases often create more questions than answers. One example is “dowsstrike2045 Python,” a term that does not immediately identify a well-known Python library, framework, or standard programming concept. When developers encounter a phrase like this, the most useful approach is not to assume what it means, but to investigate its context.
The term could represent a project name, username, repository, script, package, filename, or a reference used within a particular online community. Understanding that distinction is important because unfamiliar code should always be evaluated based on verifiable information rather than the name attached to it.
This guide explains how to approach dowsstrike2045 Python, what to look for when researching an unfamiliar Python project, and how to examine code without unnecessarily exposing your computer or data to risk.
What Is dowsstrike2045 Python?
There is no broadly recognized Python language feature called “dowsstrike2045.” Python itself is a general-purpose programming language used for web development, automation, data analysis, artificial intelligence, scripting, cybersecurity research, and many other applications.
As a result, dowsstrike2045 Python is best treated as a potentially project-specific or context-specific term unless reliable documentation establishes otherwise.
The surrounding information matters. For example, a search result containing the term alongside GitHub could indicate a repository or developer account. A result mentioning PyPI could point toward a Python package. A reference inside a tutorial could instead describe a particular script or coding project.
Without that context, attaching a specific technical meaning to the phrase would be speculative.
Why Unfamiliar Python Terms Require Context
Python has a huge ecosystem containing millions of projects, packages, scripts, tutorials, repositories, and developer-created tools. Not every project has broad documentation or widespread recognition.
A distinctive name can refer to several different things:
A GitHub Repository
A developer may create a repository using an unusual name. The repository could contain Python scripts, documentation, configuration files, or an experimental project.
The repository’s README, commit history, file structure, and license can provide considerably more information than the project name alone.
A Python Script
The phrase could also identify a standalone .py file. A script might automate a repetitive task, process data, interact with an API, or perform another specialized function.
In this situation, the actual source code is more informative than the filename.
A Username or Developer Alias
Some technical projects are associated with usernames rather than formal software brands. If “dowsstrike2045” appears as an account name, the Python connection may simply indicate that the account publishes or discusses Python-related material.
A Package or Dependency
If the term appears in a Python installation command or dependency list, it is worth checking whether it corresponds to a package available through a recognized package repository.
However, developers should not install an unfamiliar package solely because a search result recommends it.
How to Research the dowsstrike2045 Python Term
The first step is to establish exactly where the term appears.
Search the complete phrase together with context-specific terms such as “GitHub,” “repository,” “Python,” “package,” or “code.” This can help distinguish a software project from an unrelated reference.
Once you locate a possible source, examine the following information.
Check the Original Source
Whenever possible, identify the original repository, package page, documentation site, or developer account.
Third-party posts can be useful for discovery, but they may contain outdated or inaccurate descriptions. Primary documentation is generally more useful for determining what a project actually does.
Examine the Project Description
A legitimate project should ideally explain its purpose.
Look for information such as:
- What problem the project solves
- Which Python version it requires
- How it is installed
- What dependencies it uses
- Whether configuration is required
- Whether the project is actively maintained
- What license applies
A lack of documentation does not automatically mean that code is malicious, but it does mean that users should be more cautious.
Inspect the Source Code
If the project contains Python files, review them before executing anything.
Pay particular attention to code that:
- Reads sensitive files
- Sends information over the network
- Executes shell commands
- Downloads additional files
- Modifies system settings
- Requests administrator privileges
- Handles passwords, tokens, or private keys
Python is capable of interacting extensively with an operating system, which makes source-code review an important step for unfamiliar scripts.
Is dowsstrike2045 Python Safe to Run?
The safety of a Python project cannot be determined from the name dowsstrike2045 Python alone.
A project’s safety depends on the actual code, dependencies, distribution method, permissions, and environment in which it runs.
This is an important distinction. A Python script can be completely harmless, potentially unsafe, or somewhere in between. The name itself provides little evidence.
Before executing unknown Python code, consider reviewing its source and checking its dependencies.
If you are unsure about a script, avoid running it directly on a computer containing sensitive information.
A Safer Way to Test Unknown Python Code
Developers often need to test unfamiliar code. The safest approach is to isolate the experiment from important personal or business data.
A disposable virtual machine or appropriately configured isolated development environment can reduce the potential consequences of a mistake.
For example, a developer might create a separate environment for a project rather than installing its dependencies globally.
Python’s virtual environments are useful for dependency isolation:
python -m venv test-environmentAfter creating the environment, activate it according to the operating system and install only the dependencies that are actually required.
However, a virtual environment is not a complete security boundary. Malicious code can still interact with the operating system, network, or other accessible resources. Stronger isolation may therefore be appropriate for genuinely untrusted software.
Why Python Dependencies Matter
One of the most overlooked risks when investigating an unfamiliar Python project is its dependency chain.
A project may contain relatively simple source code while depending on several external packages. Those dependencies can introduce additional functionality and additional security considerations.
Before installing a package, check:
Package Name
Make sure the package name is exactly what the documentation specifies. Attackers can sometimes exploit confusingly similar names.
Source and Maintainer
Look for the project’s official repository and maintainer information.
Version Requirements
Old projects may depend on outdated Python versions or libraries. Installing incompatible dependencies can create unexpected behavior.
Installation Instructions
Be cautious when documentation asks users to execute commands copied directly from unknown sources, particularly commands that download and execute additional software.
Understanding Python Code Before Running It
Even developers who are comfortable with Python can benefit from a structured review process.
Start with the entry point of the application. Determine what happens when the program launches.
Then trace important functions and identify external interactions.
For example, a script that performs ordinary calculations may require very little scrutiny. A script that accesses files, communicates with remote servers, or executes operating-system commands deserves substantially more attention.
Some Python modules deserve particular scrutiny when encountered in unfamiliar code.
These include modules and functions related to process execution, file operations, networking, and dynamic code execution.
The presence of one of these capabilities does not automatically make a program malicious. Legitimate software frequently needs them. The important question is why the program uses them and what information or permissions it receives.
Common Mistakes When Searching for Unknown Python Projects
People investigating unusual programming terms often make the same few mistakes.
Assuming the Name Defines the Function
A project name may have nothing to do with what the software actually does. Always examine documentation and source code.
Installing Before Investigating
Running an installation command is not a substitute for research. Review the project first.
Trusting a Random Download
A search engine result or file-sharing page may not represent the original developer’s work.
Ignoring Dependencies
The main script is only part of the software supply chain. Dependencies deserve attention as well.
Using Sensitive Credentials During Testing
Avoid supplying production API keys, passwords, private certificates, or other sensitive information to an unfamiliar application.
How Developers Can Evaluate an Unknown Repository
A simple checklist can make the investigation much more systematic.
First, identify the original source. Then review the README and project structure. After that, inspect the dependency files and important Python modules.
Next, determine whether the project has a clear purpose and whether its behavior matches its documentation.
It is also useful to examine recent project activity. A repository with regular maintenance may provide more transparency than an abandoned project, although activity alone does not prove software safety.
Finally, test unfamiliar code in an appropriately isolated environment before considering it for regular use.
dowsstrike2045 Python and Search Intent
Someone searching for dowsstrike2045 Python may have encountered the term in a repository, video, forum post, code snippet, software download, or social media discussion.
That makes the search intent potentially ambiguous.
Some users may want to know:
- What dowsstrike2045 means
- Whether it is a Python project
- Where the source code is located
- How the project works
- Whether a related Python script is legitimate
- How to install or run the software
- Whether the project has documentation
The correct answer therefore depends heavily on the original context where the phrase was discovered.
Rather than inventing a specific definition, researchers should identify the source first and then verify the project’s actual purpose.
Frequently Asked Questions
What is dowsstrike2045 Python?
“dowsstrike2045 Python” does not describe a standard Python language feature. It appears to be a context-specific term whose meaning should be established from its original source, such as a repository, package, script, or developer account.
Is dowsstrike2045 a Python library?
The name alone is not enough to establish that it is a Python library. A library should be verified through its official documentation or package repository.
Can I run a dowsstrike2045 Python script?
Only run an unfamiliar Python script after determining what it does and reviewing its source and dependencies. If the source is not trustworthy, test it in an isolated environment rather than on a system containing sensitive information.
How can I find the original dowsstrike2045 project?
Search the exact term alongside context such as “GitHub,” “Python repository,” “PyPI,” or “source code.” Compare results and prioritize the original developer or project documentation.
Does an unusual Python project name mean the software is dangerous?
No. An unusual name is not evidence that software is malicious. Safety depends on the actual code, dependencies, permissions, and behavior of the application.
What should I check before installing an unfamiliar Python package?
Check the exact package name, source, maintainer, documentation, dependencies, version history, and installation instructions. Avoid blindly executing commands from unverified sources.
Are Python scripts automatically safe because Python is widely used?
No. Python is a programming language, not a security guarantee. Any programming language can be used to create harmless, questionable, or malicious software.
Can a Python project access my files?
Python programs can interact with files when the operating system and application permissions allow it. The specific behavior depends on the code being executed.
Should I use my main computer to test unknown Python code?
For genuinely untrusted code, using an isolated testing environment is safer than running it directly on a primary computer. The level of isolation should match the potential risk.
What is the most important thing to remember about dowsstrike2045 Python?
The name should not be treated as proof of what the project is or what it does. Find the original source, inspect the documentation and code, verify dependencies, and understand the program before executing it.
Conclusion
The phrase dowsstrike2045 Python does not, by itself, provide enough information to establish a specific Python technology or project. It may refer to a repository, script, package, username, or another context-specific resource.
The most reliable way to investigate it is to start with the original source and evaluate the available documentation, source code, dependencies, and project history. Developers should be especially careful before executing unfamiliar code or providing it with access to sensitive files, credentials, or network resources.
When an unusual programming term appears in search results, the goal should not simply be to find a quick installation command. A better approach is to understand what the software is, where it came from, what it does, and whether its behavior matches its stated purpose.

1 Comment
Pingback: Obituary Debby Clarke Belichick: What Is Actually Known About Her Life and Family?